Revolut is confronting a ransom demand after hackers gained access to sensitive customer data through a sophisticated impersonation scam. The attackers reportedly used a legitimate government agency email domain to submit fraudulent requests for information, which Revolut then fulfilled.
The fintech confirmed the breach on September 12th, stating that a "limited" number of customers were affected. The exposed data may include names, dates of birth, occupations, postal and email addresses, telephone numbers, copies of identity documents such as passports and driver's licenses, verification selfies, account statements, IBANs, withdrawal records, and complete transaction histories, including Bitcoin activity. Passwords, card PINs, and cryptocurrency private keys were reportedly not compromised.
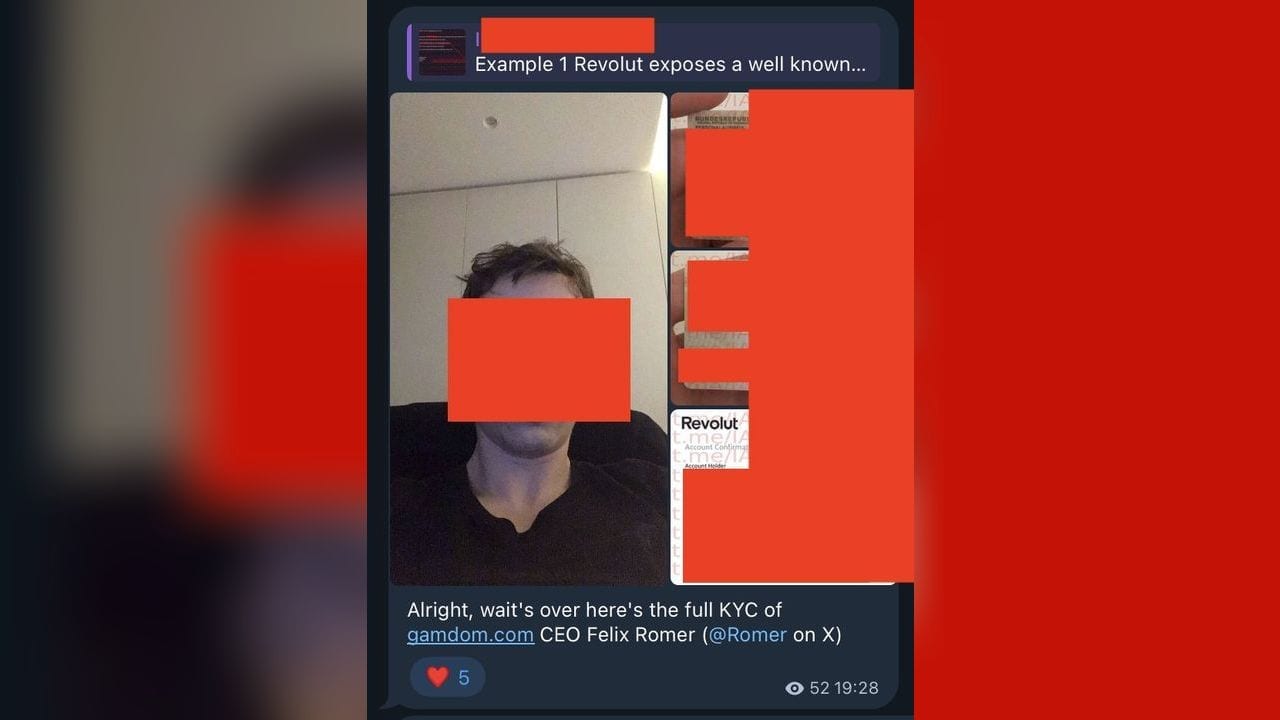
On September 13th, a group claiming responsibility for the fraudulent requests began publishing what they allege is customer identity data on X, threatening daily releases until a payout is made. Screenshots shared online show partially obscured identity documents and customer verification photographs. One alleged target named is Felix Romer, founder of crypto gambling platform Gamdom and marketplace Skins.com, with his know-your-customer file reportedly included.
Revolut stated that its systems and customer funds remain unaffected. The company has blocked the unauthorized email address, alerted the relevant government agency, law enforcement, and regulators, and directly contacted affected customers. The incident highlights the persistent risk associated with exposed know-your-customer (KYC) files, which can be used for impersonation and targeted phishing attacks.