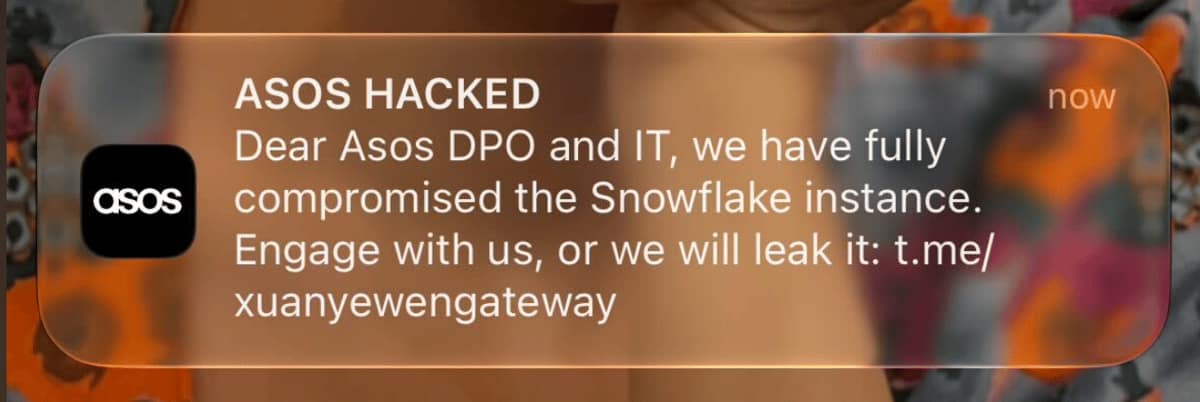
Customers of the online fashion retailer ASOS received a concerning push notification on October 6, claiming the company's Snowflake instance had been compromised and threatening to leak data. The message, signed 'xuanyewengateway', directed recipients to a Telegram channel.
ASOS confirmed it was investigating unauthorized activity involving third-party platforms used for customer communication. The company stated that basic personal information, including names and contact details, may have been accessed. However, ASOS does not believe that payment card information or account passwords were impacted. The retailer's website and app are operating normally, with no disruption to its operations.
Snowflake, the cloud-based data platform used by ASOS, stated that it began an investigation upon becoming aware of the notification and has found no compromise of its platform at this time. Experts, such as Jake Moore, global cybersecurity advisor at ESET, warned that if confirmed, the incident could be significant, noting that the ability to send a push notification suggests access to connected systems, potentially to apply pressure for ransom.
The 'Xuanye Group' on Telegram, linked in the notification, claimed that payment information was not affected and that the ASOS app remained safe to use.